Supplier Cyber Incidents: How to Manage Procurement and Continuity Decisions
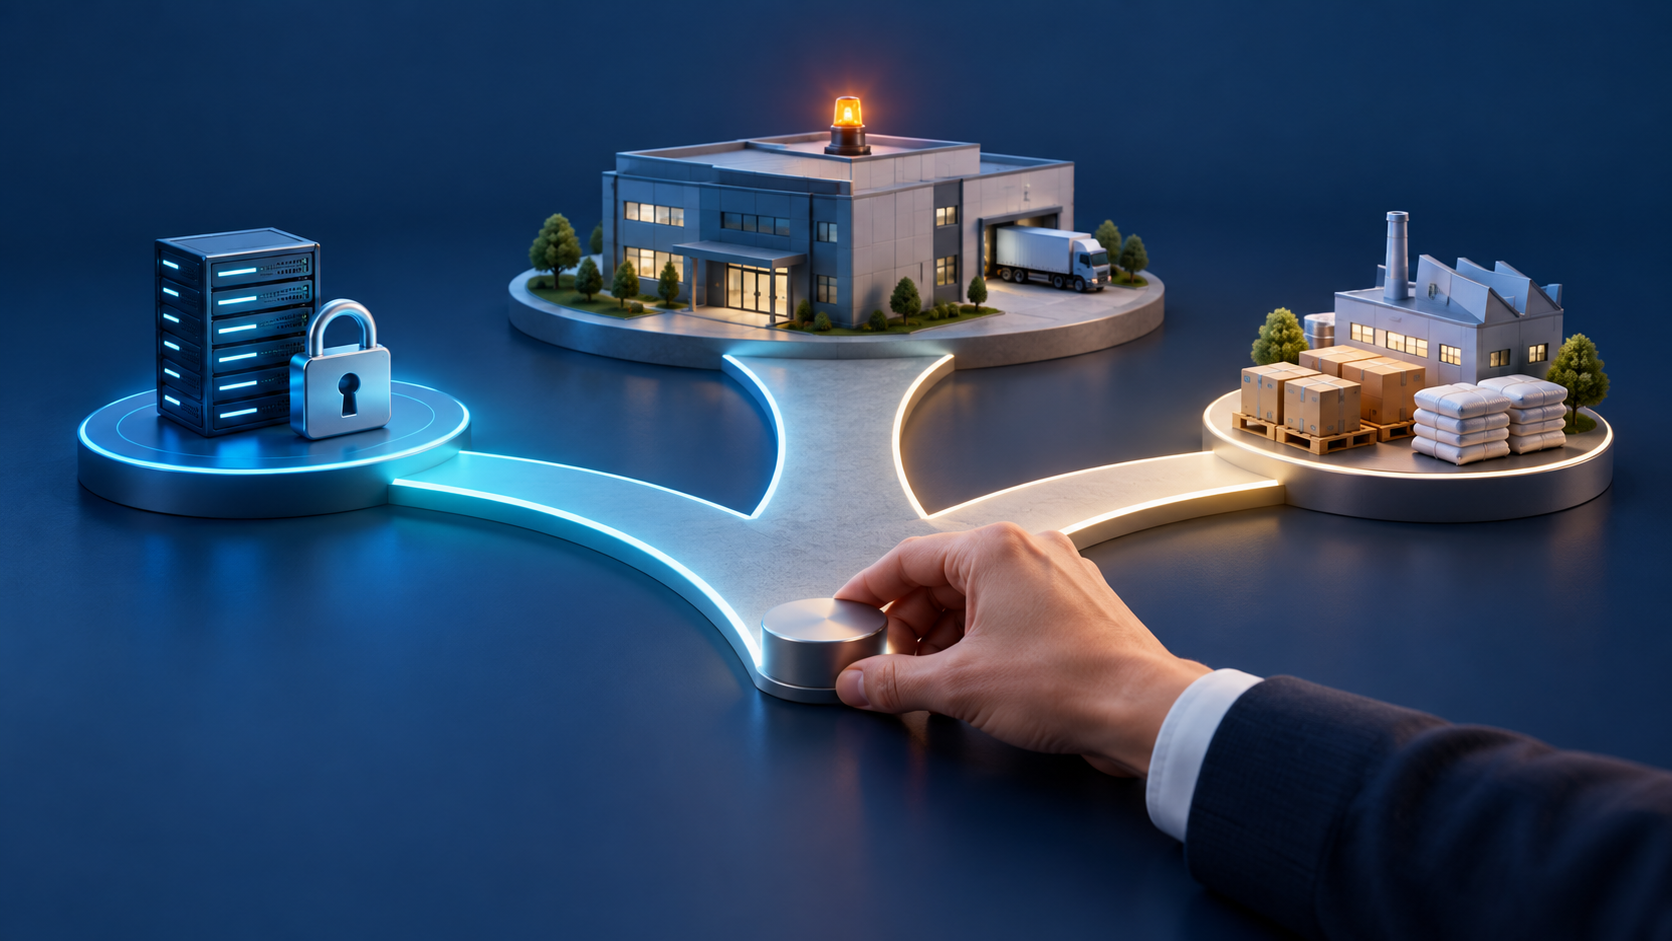
A supplier cyber incident does not affect every order equally. Verify the event, separate system access from delivery and critical-input exposure, and choose a documented response.
What should procurement do when a supplier cyber incident is reported? First verify whether it affects the correct company and the service or material you buy. Then assess two separate questions: is access to your systems or data exposed, and has the supplier's delivery or service commitment changed? Bring the security team's access decision and procurement's order or alternative-supply decision into one documented rationale. A single news report is not sufficient evidence to stop every order.
Separate incident verification from business impact
A supplier's customer portal may be unavailable while production and shipping continue. The reverse is also possible: the portal works, but a planning or warehouse outage affects delivery. These illustrative situations share the same incident label but require different procurement actions. Retain the company statement, your security assessment and the supplier's written operational confirmation as separate evidence. Do not record an unconfirmed scope or recovery date as an established fact.
NIST's SP 1326 quick-start guide, finalized on 8 July 2026, recommends prioritizing supplier due diligence by criticality and validating findings against multiple sources where possible. Its scope is information and communications technology suppliers. An operational lesson for procurement is to match review depth to the supplier's business role; it should not be presented as a mandatory legal rule for every material supplier.
- Identity and scope: does the affected legal entity, site, service or product match your purchasing relationship?
- Evidence status: is the incident confirmed or under investigation, and which information is only an estimate?
- Operational confirmation: which of production, warehousing, shipping, order confirmation and support services are affected?
- Next update: who is the authorized contact, and when is the next confirmation expected?
Assign separate owners for access and delivery decisions
Procurement should not assess the access implications of a cyber incident alone. Security and IT teams review supplier connections and shared data, and make any access restriction decisions within their authority. Procurement gathers contractual notification terms, service scope and written delivery confirmation. Continuity or planning teams assess how long disruption to the affected service or input can be tolerated.
The UK NCSC's supply chain security guidance recommends clear contractual responsibilities, reporting timescales and contacts for security incidents. This supports an established communication route rather than building one during an incident. Applicable reporting obligations and deadlines for your organization still require assessment against the relevant contract and law.
Quibas Market & Company Intelligence brings public risk and company data together with the organization's operational data, making observation and update times, confidence and decision history visible. Reading a verified company signal in this context helps explain which supplier relationship warrants review. The authorized security team determines the incident's technical scope and safe-access decision; procurement assessment proceeds with those confirmations.
Connect delivery uncertainty to critical inputs
The decisive procurement question is which commitment the incident affects. Compare the open order's required date with current delivery confirmation, inventory coverage and the time needed to activate an alternative. For an IT service, assess the critical function, tolerable disruption and verified fallback arrangement instead. Use suitable decision criteria for each relationship rather than scoring material delivery and digital-service disruption with the same unit.
ENISA's June 2023 good-practice report uses context from a 2022 study and addresses assessing supply chain risks against business continuity requirements and identifying important IT/OT dependencies. Its practices underpin this guide; its data is not used as a measure of current incident volumes or today's threat level.
- If delivery dates are unchanged and access review continues, monitor order continuity with written confirmation; do not present the review as an actual delay.
- If delivery confirmation is unavailable, use inventory coverage and required dates to set the next decision deadline.
- If fallback operation for a critical service is unverified, confirm a feasible continuity plan with the business owner and IT.
- If alternative preparation is needed, review quality and security approvals, activation time and extra cost alongside the commercial decision.
Quibas Inventory Risk & Supply Continuity assesses inventory days, confirmed receipts, lead time and supplier dependence within one risk window, turning a threshold breach into an action with an owner and follow-up date. Reviewing updated supplier delivery confirmation in this operational view helps prioritize inventory allocation or alternative preparation for verified material-flow effects of a cyber incident. The evidence that changed the decision and the approving person should remain clear.
Require evidence before lifting temporary measures
A supplier statement that systems are back online does not establish that every check is complete. The security team should assess the evidence required for safe access, while procurement reviews the updated service or shipping commitment. Record the condition for lifting a temporary measure, the required evidence and the next review date. Reassess the earlier decision if the incident recurs or its scope changes.
Start with one critical supplier relationship. Exercise the notification route, access decision owner, delivery confirmation, fallback operation and commercial approval in the same tabletop scenario. Judge success by visible outstanding questions, owners and decision deadlines from verification to a reasoned decision, rather than by alert volume.